Insurance and financial implications of FranceCyber attack on supermarket refrigeration
In the supermarket store, it’s generally a good idea to keep things cool. When a cyberattack reportedly affects refrigeration systems, the consequences could go far beyond a few melted ice creams. The recent incident in French supermarkets raises complex questions about insurance coverage and, equally important, how to price the resulting financial losses.
What happened?
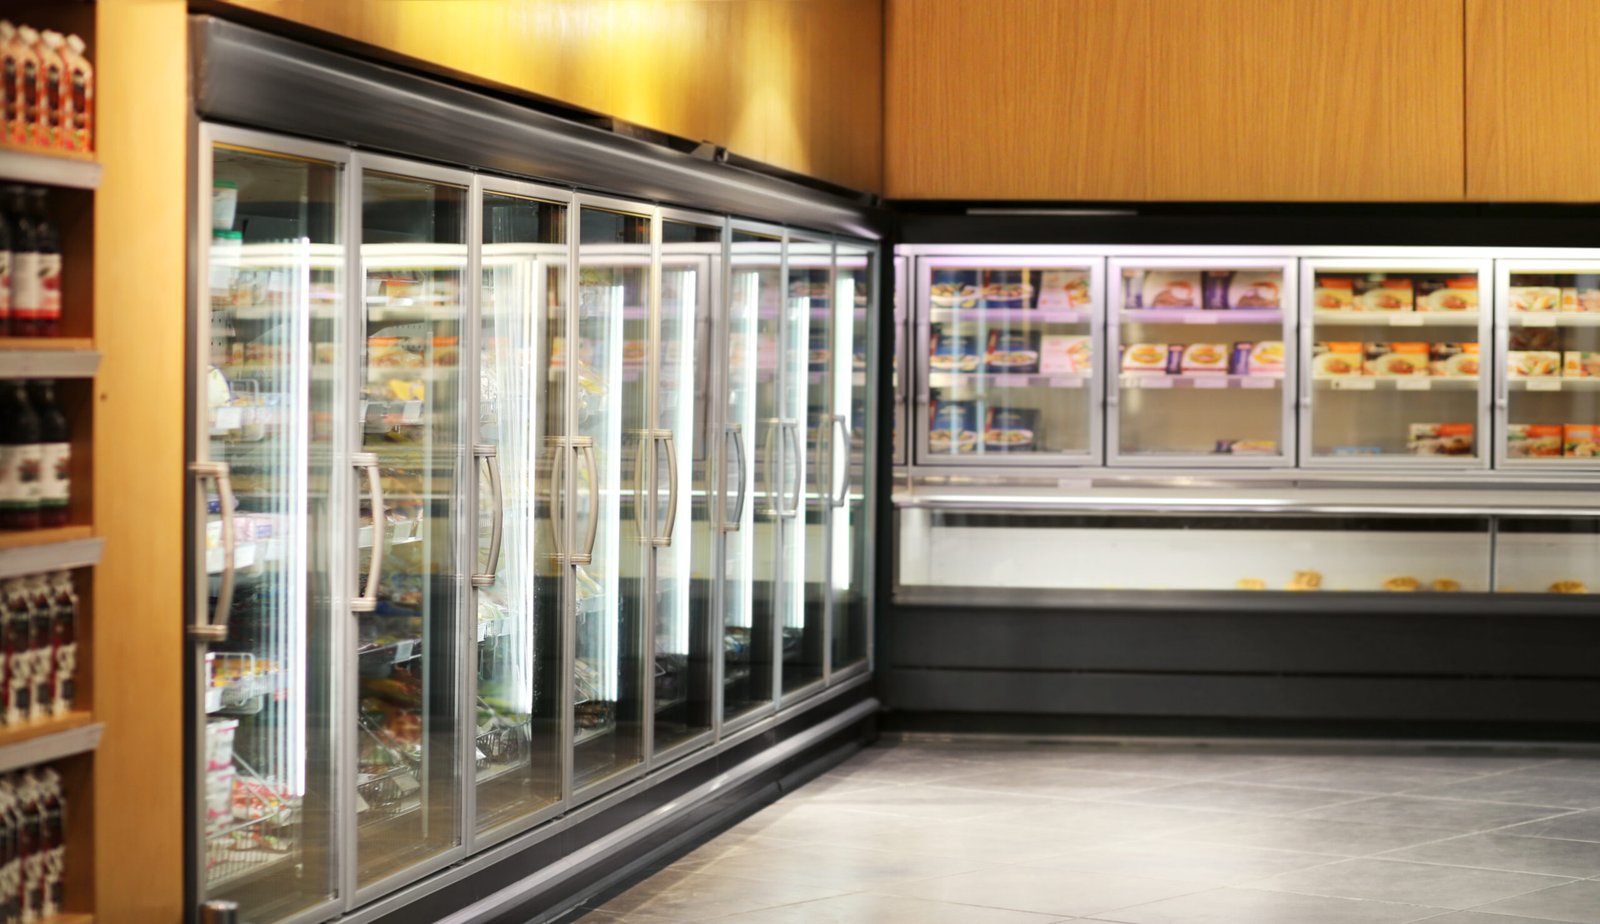
Attackers took over the refrigerators in hundreds of French supermarkets in a cyberattack that highlighted how vulnerable internet-enabled systems can be. Using the units’ direct internet connection, the attackers manually changed the temperature settings on refrigerators in several supermarket groups. According to some reports, the hackers were able to remotely increase the temperature of the refrigerators, and in some cases the devices reached temperatures as high as 50°C (122°F) and even started fires. This is a fairly rare example of a cyber incident that results in physical damage.
To date, no ransom or other demand has been made and no group has publicly claimed responsibility. Around 350 supermarkets in France were affected. The cooling units ran on software from the Danish company Danfoss. Many of the compromised devices were past the end of their lifespan, meaning they no longer received software or security updates or were equipped with outdated firmware.
A similar attack hit a retailer in the Netherlands. The Dutch company also operates several U.S. grocery chains, including Stop & Shop and Giant Food.
Which insurance applies: Cyber, PRoperty, Both or Neither?
Is this damage insured under cyber or property insurance? Possibly both – or neither. Many property insurance policies now include cyber exclusions, sometimes with exclusions for resulting fire damage. Spoilage of refrigerated supplies is often only covered by insurance or equipment failure insurance, which may pose its own limitations related to cyberattacks.
To the extent that the answer is cyber, the key question is whether these grocers have purchased such insurance coverage. Sources suggest that cyber insurance penetration in France lags significantly behind the US, particularly among smaller companies. Even in the US, cyber insurance adoption by small businesses is estimated to be around 50%.
Inventory losses, business interruption and increased costs
The most obvious consequence of a cooling failure is spoiled supplies. Quantifying the damage is not necessarily as easy as counting the contents of the freezers. This raises a number of questions: Should the stock be valued at the cost incurred by the grocer? Should it be valued at retail price? Does it have any residual value? And how can you avoid a double claim for damages if the insurers also cover lost business interruption losses?
In such circumstances, it may be difficult for insured parties to determine losses due to business interruption, particularly if supermarkets remained open while certain departments were temporarily closed or operating at reduced capacity.
Finally, a customer who is unable to purchase a frozen pizza could opt for a fresh pizza instead, visit another supermarket (perhaps within the same retail group), or simply come back when the freezers are operational again. Not every lost frozen food sale necessarily results in a dollar-for-dollar decline in profits.
A decline in sales cannot simply be multiplied by the supermarket’s accounting gross margin to determine the insurable loss. Depending on contract wording, adjustments may be required for uninsured labor costs, variable cost savings, and differences in contribution margins between product categories.
Even if the cooling system is operational again, the financial consequences may still remain. Replenishing stocks, restoring product ranges and returning to normal trading may take time, while temporary cooling, accelerated deliveries and other mitigation measures may drive up costs.
Exclusions, business interruption triggers and attribution
Cyber policies often exclude “physical harm and bodily harm.” Does this exclusion apply to inventory loss or property damage caused by resulting fires or property damage to the equipment itself? Some cyber policies provide exceptions to such exclusions that would restore coverage to “bricked” hardware rendered unusable by an attack. If this language were present here, it could respond to damage to the controls, if not the cooling units themselves. Under U.S. law, depending on the state and policy wording, this issue could be related to the efficient proximate cause doctrine and raise questions about whether the primary cause of the damage was the cyberattack, loss of cooling, or an intervening fire. However, the policies of the affected grocers are likely to be governed by French law, which requires exclusions to be clear and limited (“formelle et limitée”) to be enforceable.
This incident also raises the question of whether the grocer’s loss of income would be covered by direct business interruption insurance or contingent business interruption insurance. It is not yet clear whether this was a coordinated, possibly automated attack on cooling controls installed in individual stores or whether it was a breach of the manufacturer’s central software infrastructure. The former would be direct business interruption coverage, while the latter would be a contingent business interruption issue. Early reports went both ways: French supermarket chain E.Leclerc attributed the disruption to an attack on one of its refrigeration equipment suppliers, while Danfoss pointed to outdated equipment at customer sites.
In the event of a business interruption, many cyber insurance policies require a written contract between the insured and the dependent company where the security breach occurred, and some limit coverage to IT service providers. Whether a refrigerator manufacturer qualifies may depend on whether it hosts or operates the remote monitoring platform. Presumably these grocers had written contracts with the refrigerator manufacturers when they purchased the equipment. But are they doing it now?
Danfoss, the manufacturer of the affected controllers, said that most of the affected devices are older models that no longer receive software or security updates, and that it has long advised its customers to update or replace them. Have these customers let their contracts expire? Do they simply operate the remote systems on their own, without an active contract with the manufacturer? This could impact coverage if the attack vector is at the vendor level. Conversely, if the attackers have exploited unsupported or unpatched devices at the branch level, insurers may point to policy conditions or exclusions that relate to unsupported software or failure to apply available security patches.
Attribution can also be important. No group has claimed responsibility, but if the attack is ultimately attributed to a state actor, insurers can rely on exclusions for war or state-sponsored cyberattacks, which Lloyd’s has required in standalone cyber insurance policies since 2023.
Separation of interim losses from normal trading
One of the challenges in assessing these claims will be distinguishing the losses that are actually attributable to the incident from the usual ups and downs of supermarket trading. Seasonality, promotions, price changes and underlying sales trends can impact sales whether freezers are in operation or not.
A forensic accounting assessment may therefore include examining point-of-sale data, departmental margins, historical trading patterns and comparable unaffected stores to determine what the incident actually cost, rather than simply assessing lost inventory or comparing forecasts with actual values.
Assignment and reclaim atowards third parties
The story may not end with the insurance claim. If investigations reveal that there are grounds for compensation from equipment manufacturers, maintenance companies or technology providers, the financial consequences could ripple even further down the chain. The higher up a vulnerability is, the more companies could be affected by a future attack and the more parties could face claims for damages as a result.
A broader operational technology problem
While some officials are describing this event as an attack on France’s food supply, the attack could be part of a broader trend in which hackers are testing the vulnerabilities of various operational technologies. In many organizations, operational technology (OT) may be less secure than IT systems.
The risk extends far beyond supermarkets: There are documented concerns that U.S. water utilities are also running critical systems with outdated software that is directly connected to the internet. These critical systems are vulnerable to the same type of remote attacks and tampering that could alter water chemistry or pressure and cause physical damage.
The conclusion
This incident raises important questions about the intersection between cyber and property risks. And it highlights the problem of operational technology being outdated and connected to the internet. When hackers can access physical devices, there is a greater risk than just data loss and business interruption. it may have health and safety implications.
From an insurance coverage perspective, a clear understanding of losses, their causes and their financial consequences is critical to managing the claims and recovery process.
Topics
Cyber profit loss